Fewer keys under the doormat: why trusted publishing matters for Open VSX
Every software registry eventually learns the same lesson: the most valuable thing in a publishing pipeline is not the code. It is the credential that lets someone ship it.
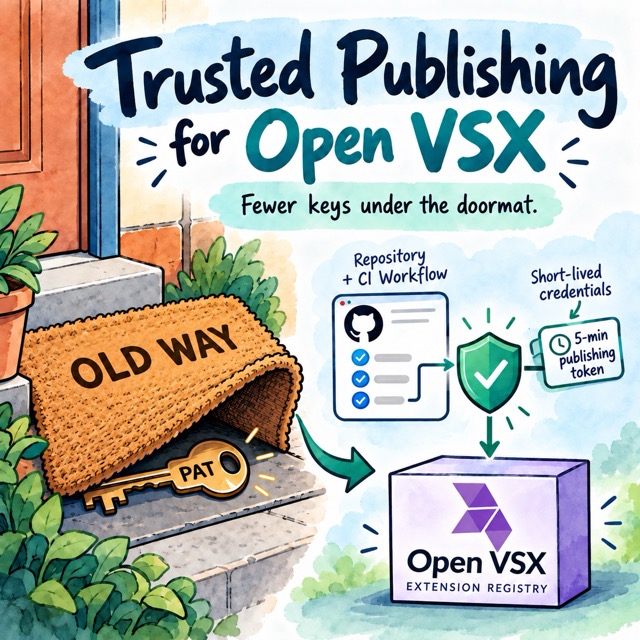
For most of its history, publishing an extension to the Open VSX Registry from CI has meant creating a personal access token and storing it as a secret in a pipeline. That token is a key left under the doormat. It works at any time, from anywhere, for whoever finds it, and it keeps working until someone notices it should not.
Trusted publishing is now available on Open VSX. Tamas Cservenak has already written a practical guide to setting it up. This post is about something else: why we think it matters, which threats it addresses, which ones it deliberately leaves to other controls, and where it fits in the way we approach the security of the registry.